
The immediate problem: connected devices outpacing protections
Manufacturers and operators in Europe and Asia now face tangible pressure to secure millions of endpoints. Vehicles, smart meters, and logistics trackers rely on SIM-based identity and connectivity; even access solutions such as the nfc car key depend on trusted credentials. The heart of the problem is clear: a secure IoT M2M sim card must offer robust provisioning, lifecycle control, and strong authentication without adding operational friction.
Why many SIM approaches are insufficient
Legacy SIMs were designed for consumer phones. M2M use requires persistent identity, remote management, and resistance to cloning. Common weak points include static IMSI usage, manual SIM swaps, and poor OTA firmware governance. eSIM or eUICC helps, but eUICC alone does not solve certificate management or PKI needs. These gaps result in service disruption, unauthorized access, and regulatory exposure.
Key technical considerations for secure deployments
Procurement teams should evaluate these technical controls when they select a solution for M2M deployments:
- Provisioning model: remote SIM provisioning (RSP) with eUICC to avoid physical swaps.
- Authentication: PKI-backed mutual authentication instead of plain IMSI checks.
- OTA management: secure update channels to patch device firmware and SIM applets.
- Roaming and supplier agreements: clear SLAs for latency, IMSI retention, and fraud response.
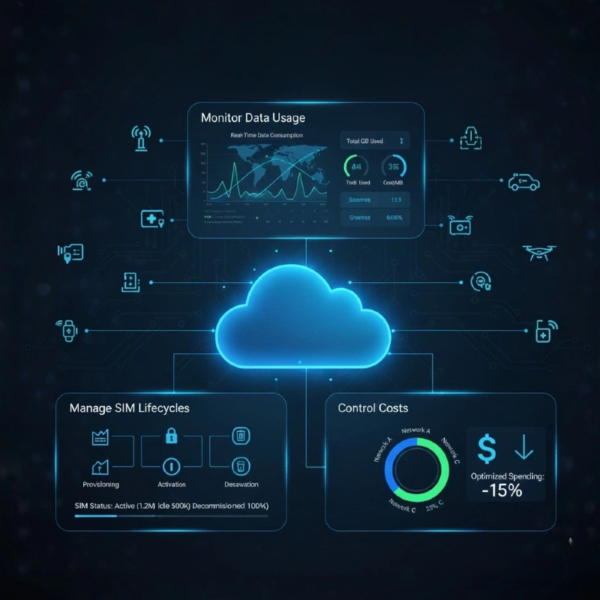
- Lifecycle visibility: dashboarding for activation, deactivation, and SIM recycling.
Consider “M2M SIM security” as an operational discipline, not just a hardware choice. Good visibility and policy are as important as cryptographic strength.
Operational patterns that work
Operators adopt one of three patterns: MNO-managed M2M profiles, MVNOs with dedicated enterprise stacks, or platform-as-a-service for global fleets. Each pattern balances control and cost differently. For high-security verticals—connected cars, industrial controls—teams favour eUICC with centralized certificate authorities and strict OTA gating. For consumer IoT at scale, MVNO stacks ease deployment but demand rigorous integration testing to prevent configuration drift.
Real-world anchor and regulatory context
Europe’s NIS2 directive tightens responsibilities for network and service operators, and Asia’s continued 5G rollout elevates device density in urban centers like Tokyo and Seoul. These developments create measurable requirements for device identity and incident reporting. In practice, an automotive fleet I advised in 2022 moved from physical SIM swaps to eUICC to reduce theft-related downtime—resulting in fewer service interruptions and faster incident remediation.
Common mistakes to avoid
Teams repeatedly underestimate three areas: lifecycle automation, supplier churn, and threat modelling. They deploy SIMs without a tested OTA path. They change vendors without migrating certificates. And they design authentication assuming the network is always trusted. Fixing these requires process work as much as technical choices—deploy a staging environment that mirrors production, and run periodic failover drills. —This often feels tedious, but it prevents expensive incidents later.
Alternatives and complementary hardware
When NFC-based access surfaces are needed, evaluate hardware that integrates secure elements with established provisioning flows; for example, pairing an NFC device to an authenticated SIM profile reduces attack surface. Some suppliers combine secure elements and network credentials to manage both local access and wide-area connectivity. Practical evaluations should include interoperability tests with devices such as nfc car keys.
Advisory: three golden rules for choosing a provider
1. Measure maintainability: ensure the provider supports staged OTA rollouts, rollback, and audit logs for at least 24 months post-deployment.
2. Verify cryptographic ownership: require PKI controls where you can either host the root CA or audit key management practices quarterly.
3. Confirm global SLA alignment: check roaming partner lists, fraud response times, and real-time session visibility, not just theoretical coverage maps.
For teams lining up a secure IoT M2M sim card strategy, these rules help narrow choices and set procurement language that is enforceable. —A short test suite and a tight contract save months of remediation.
Small, tangible steps—provisioning discipline, OTA governance, and verified PKI—deliver the resilience modern fleets require. BHDC.